The EU AI Act’s risk-tier system, banning unacceptable uses, tightly regulating high-risk ones, and requiring transparency for the rest, legally applies to any organization whose AI systems or outputs touch EU citizens, regardless of where that organization is headquartered. But even companies with no EU customers are increasingly adopting it as their internal governance baseline, because it’s one of the few detailed, well-reasoned frameworks for classifying AI risk that already exists. Adopting it saves companies from building that framework from scratch, which matters more than the compliance angle for most of them.
The EU AI Act was written to govern AI inside the EU. In practice, it’s shaping how organizations everywhere think about AI risk, whether or not they have a single employee or customer on the continent.
Part of that is legal reality. The Act’s territorial scope isn’t limited to companies based in the EU: it applies to any provider that places a high-risk AI system on the EU market, and to any provider or deployer outside the EU whose AI system’s output is used within the EU. A company headquartered anywhere in the world can fall under the Act the moment its AI touches an EU customer, employee, or user.
That’s the piece Merav Yuravlivker, Chief Learning Officer and Co-Founder of Data Society, sees organizations underestimate:
“With the EU AI Act and the risk levels that they have put into place, whether you are located in Europe or not, it would be best practice to adhere to how they evaluate risk around implementing AI. Obviously, if you have customers in Europe or you’re doing work in Europe, it’s imperative to get your procedures and your governance in place to align with the EU AI Act. But even if you don’t, they’re setting a standard and they’re providing a lot of definitions for organizations that may not have had the time or the expertise to develop it on their own.”
Merav Yuravlivker, Chief Learning Officer and Co-Founder, Data Society
For companies actually doing business in the EU, that’s a compliance deadline. For everyone else, it’s something closer to a free framework: a detailed, already-negotiated set of definitions for what counts as high-risk AI, built by people who spent years arguing over the edge cases so individual companies don’t have to.
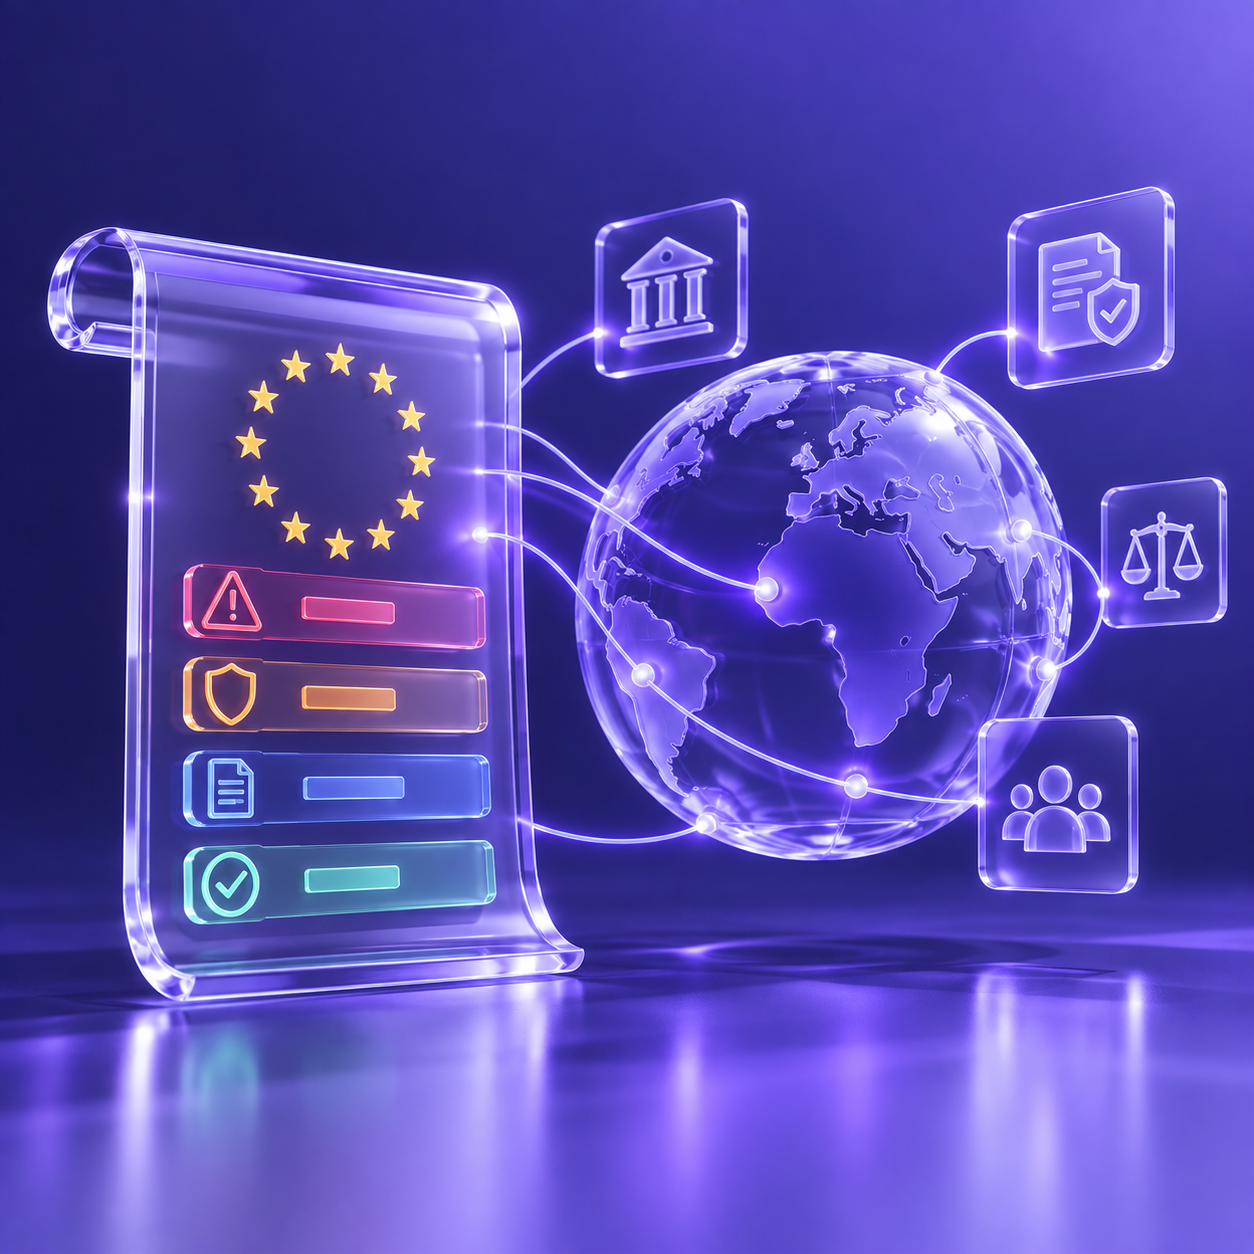
The Act sorts AI systems into four tiers, and the obligations escalate sharply as the risk does.
Unacceptable-risk systems are banned outright: AI that manipulates vulnerable people, enables government-style social scoring, or performs real-time biometric identification outside narrow, court-approved law enforcement cases. This category took effect first, in February 2025, and was expanded this year to explicitly cover AI-generated non-consensual intimate imagery.
High-risk systems are the core of the framework: AI used in healthcare, hiring, credit and lending, education, critical infrastructure, and law enforcement, the categories where a bad output doesn’t just waste time, it can cost someone a job, a loan, or medical care. These systems require pre-market risk assessments, registration in an EU database, ongoing monitoring, and a Fundamental Rights Impact Assessment before deployment. Notably, the compliance deadline for these obligations was recently pushed from August 2026 to December 2027 for stand-alone high-risk systems, after regulators concluded the technical standards needed to implement them weren’t going to be ready in time. The delay changed the calendar. It didn’t change the definitions, or the expectation that this is where serious governance needs to start.
Limited-risk systems, general-purpose models and anything that interacts directly with people, carry transparency duties: disclosing that a user is talking to AI, publishing summaries of training content, and labeling AI-generated media. Most of these obligations are already active as of this year.
Minimal-risk systems, spam filters, game AI, basic inventory tools, carry no mandatory obligations at all.
Non-compliance isn’t a slap on the wrist, either. Fines for deploying banned practices run up to €35 million or 7% of global annual turnover, whichever is higher. Even lower-tier violations, like misleading disclosures, can carry seven-figure penalties.
Regulation usually gets discussed in terms of burden: what it costs to comply, what it slows down, what it’s designed to prevent. Yuravlivker’s take on this one is different.
“What I really love about this piece of legislation, and I don’t say that very often, is that it comes from a place of good intent and a place of protection, trying to protect citizens of the EU around rampant AI usage, around high-risk usage that impacts decisions that really impact other people’s lives around healthcare and finances and things like that. So being able to put all of these checks in place, and having that governance, and being able to spread that across the organization will make you a better organization, whether you are based in Europe or not.”
That reframes the question most companies are asking, from “are we legally required to comply” to “would our AI governance be better if we did this anyway.” For most organizations building or deploying AI in healthcare, finance, hiring, or anything that shapes a real decision about a real person’s life, the honest answer is yes.
You don’t need EU exposure to borrow the structure. In practice, that means:
Classify your AI systems by risk tier internally, using the Act’s categories even if you’re not legally bound by them. Most organizations have never done this exercise at all, so simply sorting “what we’ve built” into unacceptable, high-risk, limited-risk, and minimal-risk surfaces problems that were previously invisible.
Apply high-risk-level scrutiny to anything touching healthcare, finance, hiring, or legal outcomes, whether or not it’s an EU user on the other end. If an AI system is influencing a decision that meaningfully affects someone’s life, the EU’s bar for pre-deployment testing and ongoing monitoring is a reasonable bar to hold yourself to regardless of geography.
Build something like a Fundamental Rights Impact Assessment into your deployment process, a documented review of who a system could affect and how, before it goes live rather than after something goes wrong.
Spread the governance across the organization, not just the AI team. Yuravlivker’s point about making “a better organization” is less about one compliance function bolting on a checklist than about a shared vocabulary for risk that product, legal, and engineering teams can all use.
Most companies will never be legally required to comply with the EU AI Act. Fewer will regret borrowing its logic anyway. Data Society’s AI Advisory work helps organizations map their AI systems against the Act’s risk tiers, and AI upskilling programs build the shared governance vocabulary across product, legal, and engineering teams.